The Car Alarm That Became a Thief’s Best Friend
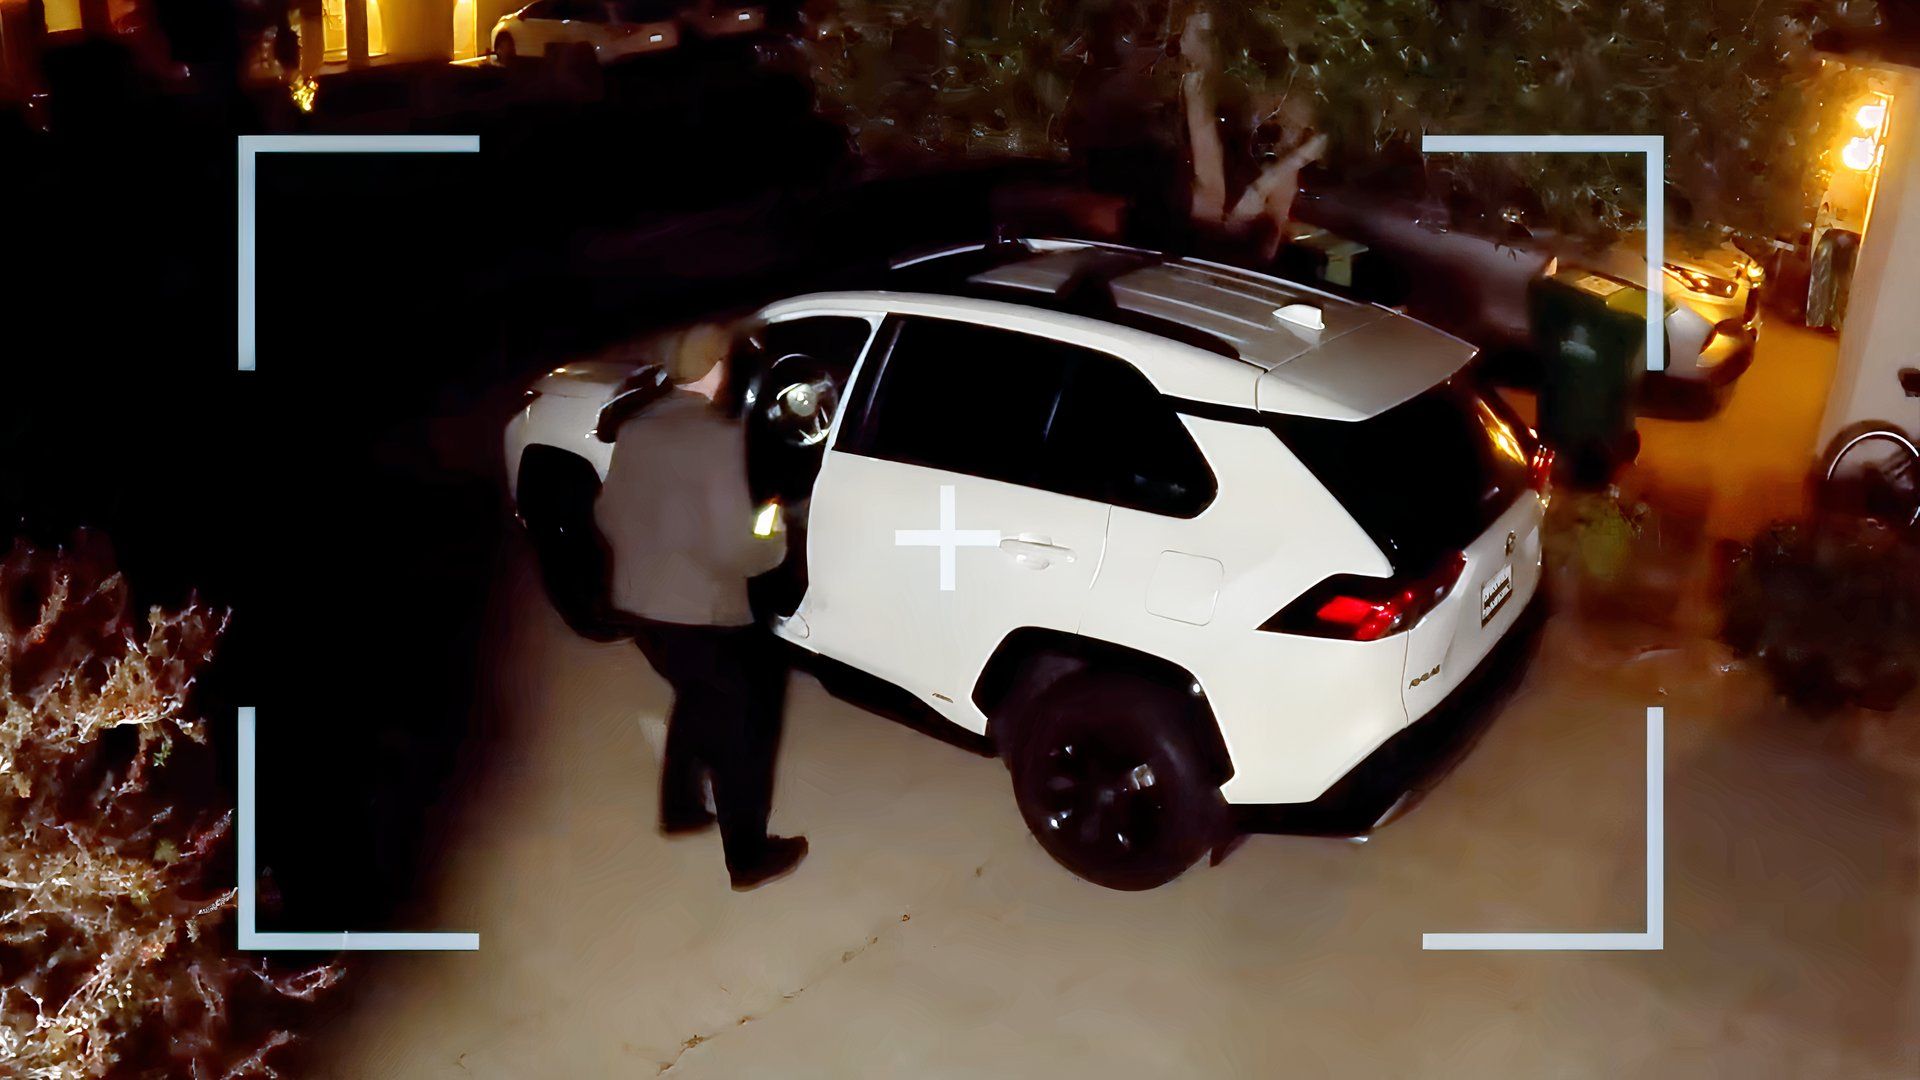
An aftermarket security system, installed in over two million vehicles across the United States, has been exposed as a massive security risk. The system, made by KARR Security Group and typically added by car dealers, contains a vulnerability that lets hackers unlock cars, disable alarms, and even kill the ignition using nothing more than a smartphone app.
Researchers at the University of Southern California discovered the flaw and demonstrated it in a video for Wired, showing how easily they could take control of vehicles they passed on the street.
The problem is compounded by the fact that most car owners have no idea the system is even in their cars. Dealers originally installed the KARR alarms to prevent thefts from their own lots. When a customer declined to buy the system as an add-on, dealers often left the hardware in place, just deactivated the app.
But the hardware remains active and can be reawakened by a simple radio command. During a 20-minute drive through San Diego, researchers logged more than 90 cars they could manipulate. The system is identifiable by a small blinking button under the dashboard or a sticker reading “KARR” or “SWDS” on the window.
KARR was notified of the flaw 18 months ago but only released a patch weeks before the researchers were set to present at the Defcon hacker conference. The company has called the vulnerability “low risk,” but researchers say the hack is trivial to replicate. The fix requires downloading the KARR app and applying an update, something most owners won’t do because they don’t know they have the system.
While the KARR system itself can’t start the car, a common locksmith tool can. Combined with the Bluetooth hack, thieves can steal a vehicle in minutes. The cars most affected are in Southern California, but the vulnerability exists in over two million vehicles nationwide.
Source: CarBuzz
Plain-English guides to common problems and what they cost in Boca Raton, plus local shops.